Introduction
Your team built an AI pilot that works. Now everyone wants it in every department. Before you approve that rollout, answer one question: who is accountable when the AI gets it wrong?
An AI governance framework gives you that answer. It sets who decides, what you check before launch, and how you catch problems after go-live. Without one, scaling AI multiplies risk faster than it multiplies value.
This guide is for CEOs, CIOs, COOs, and board members. It skips the theory and gives you the tools to act: a readiness checklist, a decision-rights table, autonomy tiers for AI agents, and a 90-day plan.
Why AI Governance Moved From IT to the Boardroom
AI no longer sits in one innovation lab. It writes customer emails, approves refunds, and triages patient requests. When it fails, the damage lands on the business, not the server.
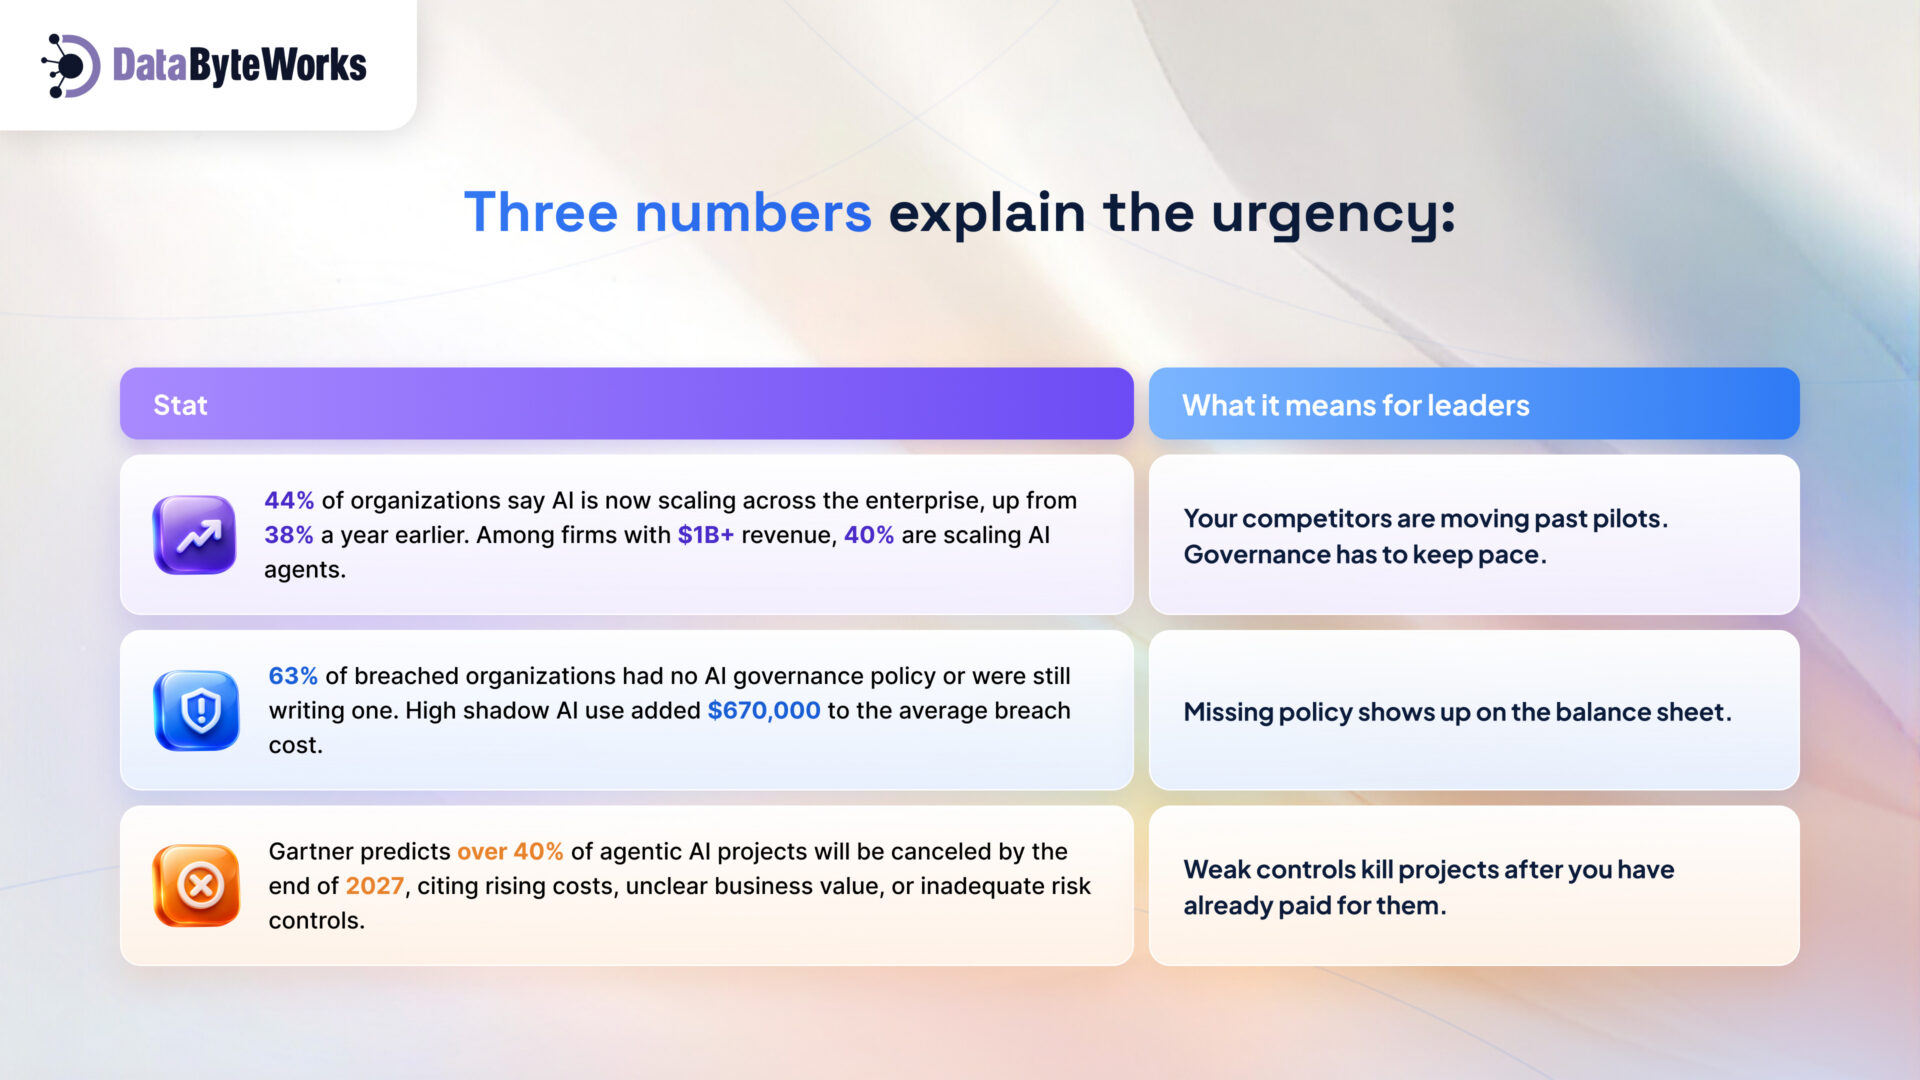
The pattern is clear. Companies that scale AI without governance pay twice: once to build it, and again to clean up after it.
What Is an AI Governance Framework?
An AI governance framework is the set of roles, rules and checkpoints that decide how your company builds, buys and runs AI. Think of it as the operating manual that keeps AI useful, legal, and safe once it leaves the lab.
It works in layers. Leadership owns accountability. Four controls then apply to every AI system, from a simple chatbot to an autonomous agent.
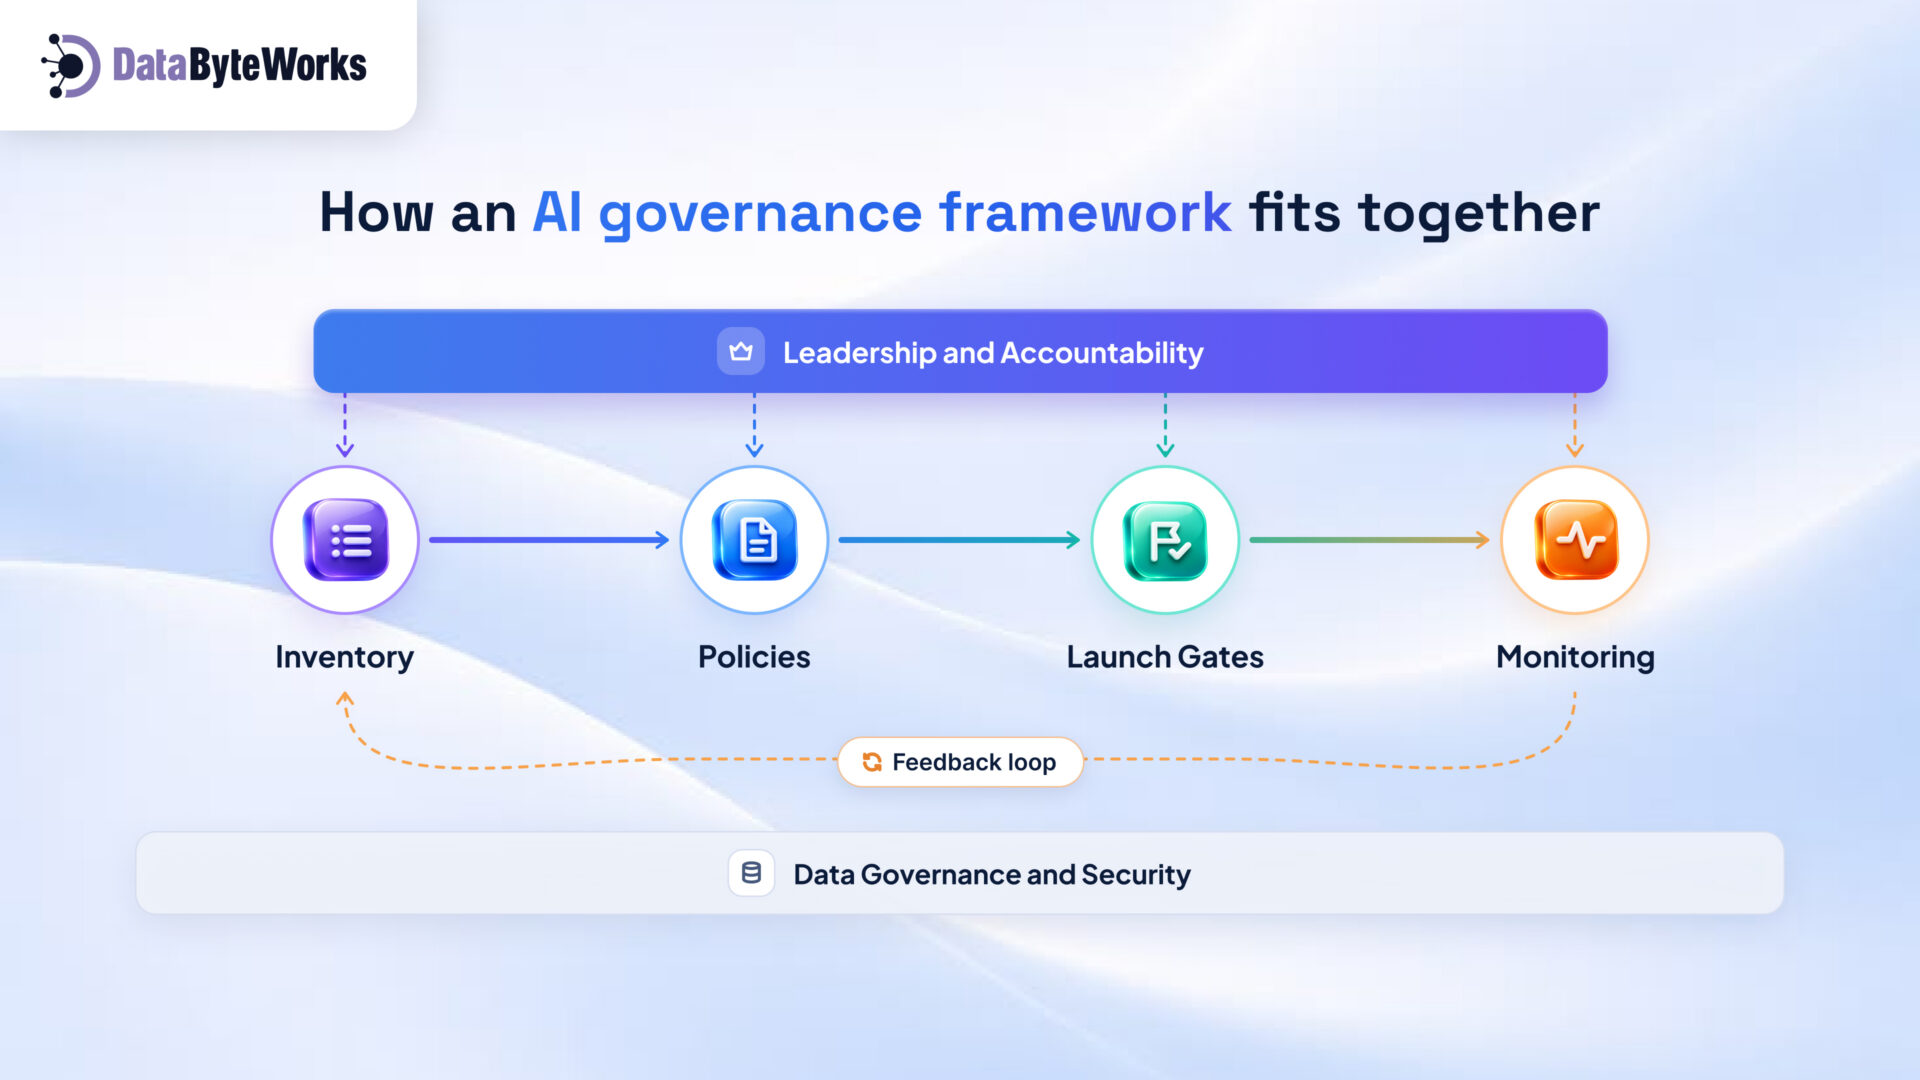
- Leadership and Accountability: The board sets risk appetite. A named executive owns each AI system.
- Inventory: A list of every AI model, app, and agent, with a risk tier for each.
- Policies: Rules for acceptable use, data handling, and vendors.
- Launch Gates: Test evidence, human sign-off, and a rollback plan before go-live.
- Monitoring: Drift and bias checks, an incident playbook and quarterly reviews.
- Data Governance and Security: The base layer that controls data access and protection.
The loop matters most. Every incident or audit finding updates the inventory and risk tiers, so the framework gets sharper over time.
AI Governance vs Data Governance
| Term | What it controls | Simple example |
| Data governance | What data you hold and who can see it | Only HR can open salary records |
| AI governance | What your AI does with that data: the decisions it makes and the actions it takes | A hiring AI cannot reject a candidate without a human review |
Why you need both: AI governance only works if your data rules are already solid. If they are still loose, start with our data governance framework guide.
The Pre-Deployment Checklist: 8 Questions to Ask Before You Scale
Most governance guides list principles like “fairness” and “transparency.” Those words don’t help you in a go/no-go meeting. Evidence does.
Use these eight questions as a gate. If your team can’t show the evidence, the rollout waits.
| # | Question to ask | Evidence to demand | Red flag |
| 1 | Do we know every AI system we run, including tools staff signed up for themselves? | A current AI inventory with owner, vendor, and data used | “We think marketing uses a few tools” |
| 2 | What is the risk tier of this use case? | A written tier (low, medium, high) with the reason | Every system rated “low” |
| 3 | Who is the named business owner? | One executive name, not a team or committee | “IT owns it” |
| 4 | What data does it touch, and are we allowed to use it that way? | Data map plus legal or privacy sign-off | Customer data sent to a public model |
| 5 | How did it perform in testing? | Accuracy, bias and failure-case results against agreed thresholds | A demo instead of a test report |
| 6 | Where does a human review or approve? | A documented approval step for high-impact outputs | Fully automated decisions on money, health or jobs |
| 7 | How do we switch it off? | A tested rollback or kill switch with a named person who can use it | No one knows |
| 8 | How will we know it is drifting? | Live monitoring dashboard and alert thresholds | “We’ll check it every few months” |
Print this table and bring it to your next AI review. It turns a vague governance discussion into a yes-or-no decision.
Who Owns What: Decision Rights for AI
Governance fails when everyone is “involved,” and no one decides. Spell out who approves, who builds, and who gets told. The table below is a starting point you can adapt to your org chart.
| Decision | Board | CEO / Exec sponsor | CIO / CTO | Legal & compliance | Business unit head |
| Set AI risk appetite | Approves | Proposes | Advises | Advises | Informed |
| Approve a high-risk use case | Informed | Approves | Advises | Must sign off | Proposes |
| Choose models and vendors | — | Informed | Approves | Reviews contracts | Requests |
| Approves go-live after testing | — | Informed | Approves | Signs off on high-risk | Accepts ownership |
| Pause or shut down a system | Informed | Can order | Can order | Can order | Can order |
| Report AI incidents | Receives quarterly | Receives immediately | Leads response | Handles regulators | Handles customers |
Notice the shutdown row. Anyone in the chain can stop a failing system. Make that explicit, or people will wait for permission while the damage spreads.
Want to know how to map this to your structure? Our AI strategy consulting team can help you set decision rights as part of your AI roadmap.
Build on the NIST AI Risk Management Framework, Not From Scratch
You don’t need to invent your own rules. Three references cover most of what regulators and enterprise customers will ask about. Pick one as your backbone and map the others to it.
| What it is | Binding? | Best use |
| US framework released January 2023, built on four functions: Govern, Map, Measure, Manage | Voluntary | Your day-to-day backbone. Plain language and easy to adopt. |
| International standard for running an AI management system, published December 2023 | Voluntary, but certifiable | Proving maturity to enterprise buyers and partners |
| Risk-based law with strict duties for high-risk AI | Mandatory if you sell into or operate in the EU | Compliance planning. In June 2026, EU lawmakers provisionally agreed to move key high-risk deadlines to 2 December 2027 and 2 August 2028, pending Council approval. |
How the NIST functions map to leadership actions
- Govern: Set risk appetite, assign owners, and approve policies. This is the decision-rights table above.
- Map: List every AI system and its context. This is your inventory and risk tiers.
- Measure: Test accuracy, bias, and security before launch, then keep measuring. This is the checklist evidence.
- Manage: Act on what you find: fix, pause, or retire systems. This is your monitoring and shutdown process.
A delayed deadline is not a reason to wait. Buyers and auditors already ask for this evidence, and retrofitting controls onto live systems costs more than building them in.
Governing AI Agents vs AI Applications
Traditional AI application development produces tools that answer. A chatbot suggests a reply. A model scores a lead. A person still decides.
AI agent development produces systems that act. An agent can send the email, issue the refund, or update the record on its own. That shift changes the governance question from “Is the answer right?” to “How much are we letting it do without asking?”
The fix is to grant autonomy in tiers. Start every agent low and promote it only when the data proves it is safe.
| Tier | What the AI does | Example | Controls before you allow it |
| 1. Assist | Suggests; a person does the work | Summarizes a contract for a lawyer | Inventory entry, acceptable-use policy |
| 2. Draft | Prepares output; a person reviews and sends | Drafts customer replies for an agent to approve | Tier 1 + output quality testing |
| 3. Act with approval | Takes action after a human clicks approve | Proposes a refund; a manager approves it | Tier 2 + approval logs, scoped permissions |
| 4. Act within limits | Acts alone inside hard limits | Issues refunds under $100 automatically | Tier 3 + spending and volume caps, live monitoring, kill switch |
| 5. Act autonomously | Plans and runs multi-step tasks across systems | Reconciles invoices across ERP and banking tools | Tier 4 + executive sign-off, full audit trail, regular red-team testing |
Most businesses should keep high-impact agents at Tier 3 until they have months of clean logs. For the technical side of limiting what agents can reach, read Your AI Agent Has More Access Than You Think. For use cases, see Agentic AI in Enterprise Workflows.
Your 90-Day AI Governance Roadmap
You don’t need a year-long program to start. Aim for minimum viable governance: enough control to scale your next AI launch safely. Then improve it every quarter.
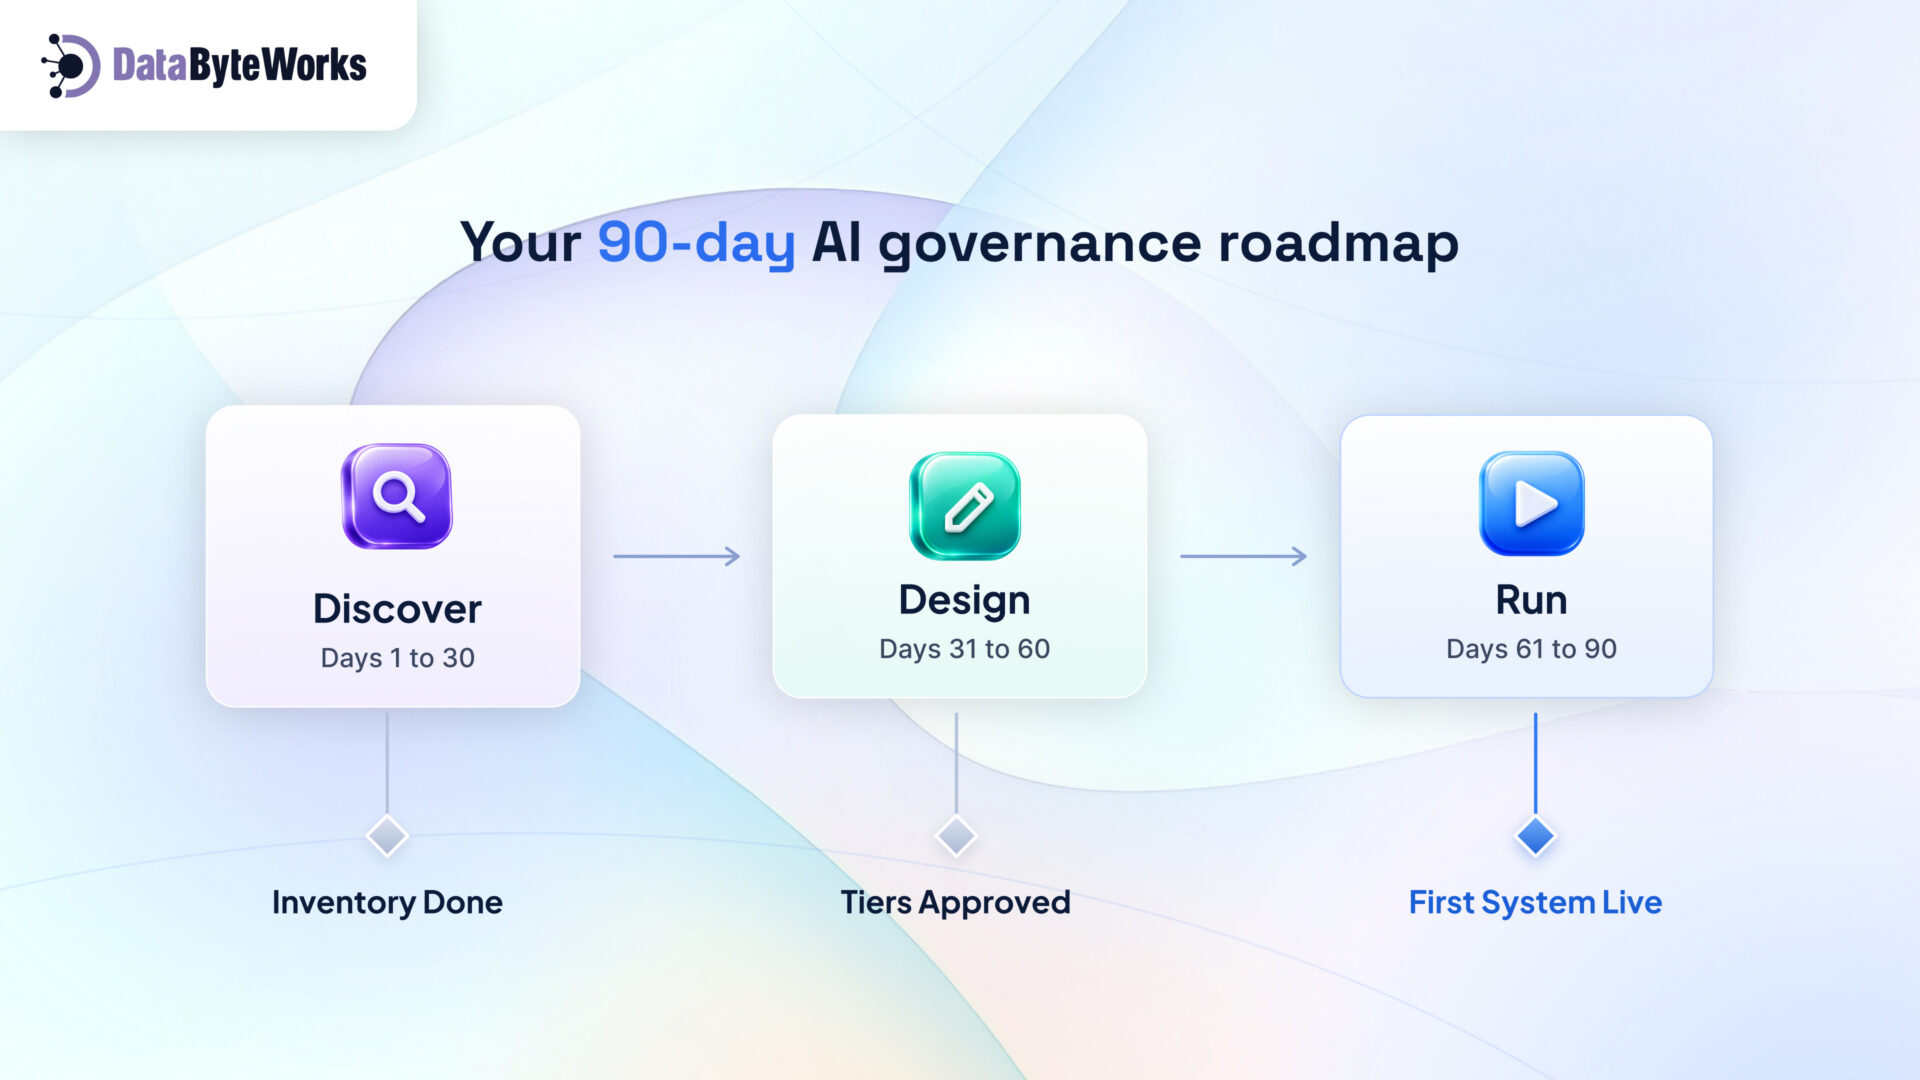
- Discover (Days 1 to 30): Inventory all AI tools, including shadow AI. Name an executive sponsor and system owners. Publish a one-page acceptable-use rule.
- Design (Days 31 to 60): Assign a risk tier to every use case. Adopt the NIST AI RMF as your backbone. Approve the 8-question launch gate.
- Run (Days 61 to 90): Send your next AI launch through the gate. Turn on monitoring and alerts. Deliver the first board AI report.
Each phase ends with a gate. Don’t start the next phase until the gate is met; that keeps the plan honest without slowing delivery.
5 Governance Mistakes That Stall AI at Scale
- Writing a policy no one reads. A 40-page PDF does not change behavior. A one-page acceptable-use rule plus a launch gate does.
- Banning AI tools outright. Staff uses them anyway, just out of sight. Offer approved tools instead, and shadow AI shrinks.
- Treating every use case the same. A meeting summarizer and a credit-decision model need very different checks. Risk tiers let low-risk work move fast.
- Governing the model, not the workflow. Most failures happen where AI meets a business process: a missing review step, a bad data feed, an unclear handoff.
- Stopping at launch. Models drift as data and users change. Without monitoring, a system that passed testing in March can fail quietly by June.
How DataByteWorks Helps You Scale AI Safely
We build governance into delivery, so your controls ship with the product instead of trailing it.
- AI strategy consulting: We help you inventory current AI use, set risk tiers, and define decision rights before you commit budget.
- AI application development: We build AI features with testing, logging, and monitoring included from the first sprint.
- AI agent development: We design agents with scoped permissions, approval steps, and autonomy tiers that match your risk appetite.
- AI integration and implementation: We connect AI to your existing systems with audit trails your compliance team can review.
Ready to scale AI without losing control?
Book a free 30-minute AI governance review with our team. We’ll look at one AI use case you plan to scale and tell you what to fix before go-live.